

How to Patch your WordPress Infected files? [STEP BY STEP]☑️
Today in this tutorial we will learn about how to patch infected files in your WordPress site.Before beginning this article you need to watch this short video tutorial on “How to Patch your WordPress Infected files”
If you want to patch your infected files found in Imunify360, then in that case follow the steps carefully:
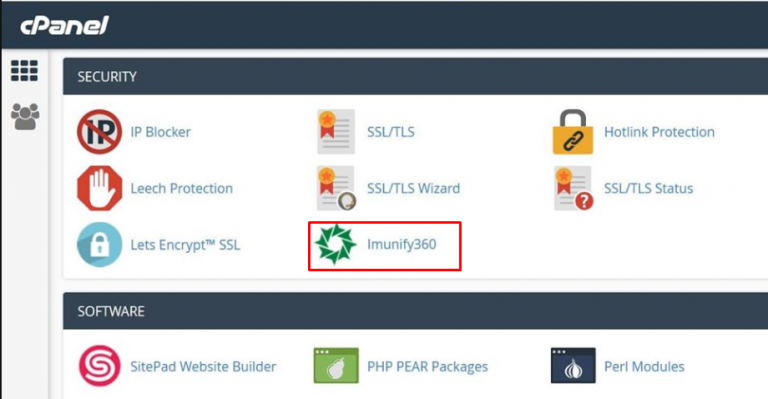
Step::1 Login to cPanel and go to Imunify 360 under SECURITY
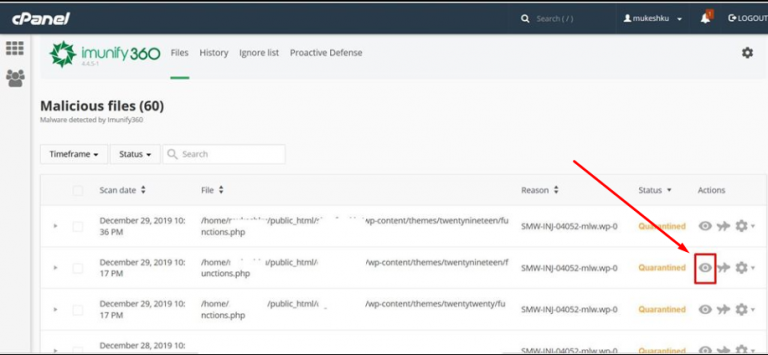
Step::2 Now go to Watch icon of an infected file
Step::3 When you click on this icon then you will find the entire code of this file.
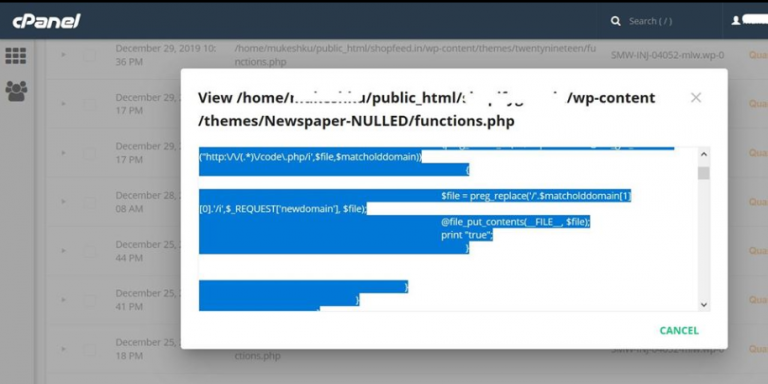
Step::4 Now here you need to understand some of the things very carefully.
Step::5 Paste the copied code in Notepad ++ and then find question mark(?) and Greater than (>) symbol in the file.
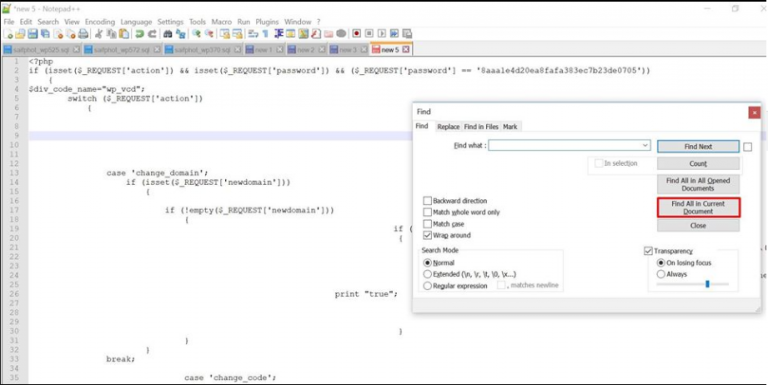
Once you do this you will find that there are two php tags, one is the php tag getting closed and again it is getting opened. This means that in most of the cases, the first code is the malicious one.
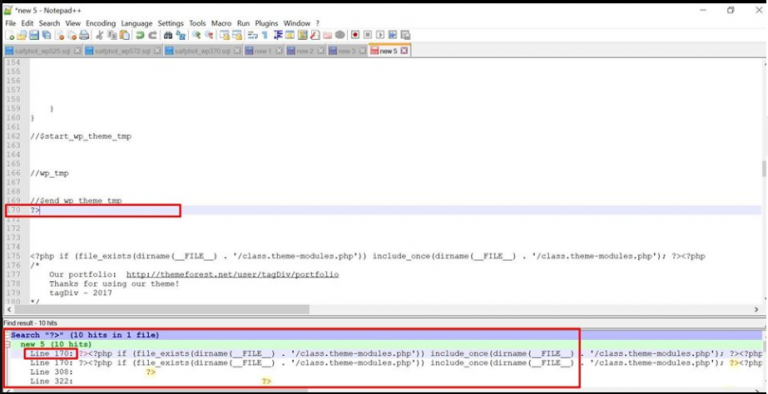
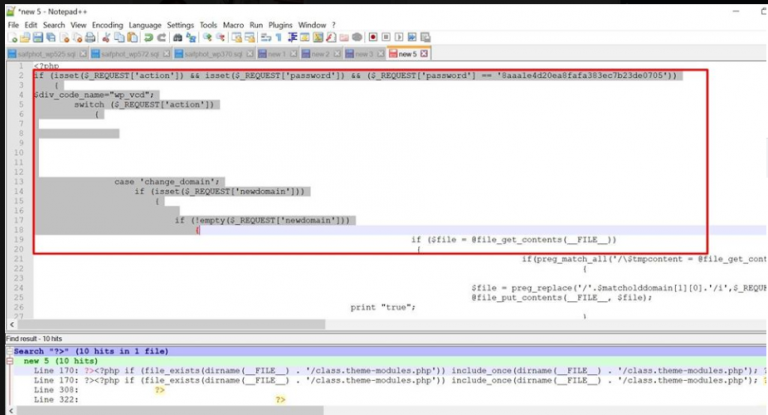
Step::6 You can manually cross check the codes, analyze it and then delete the first part of the php code.
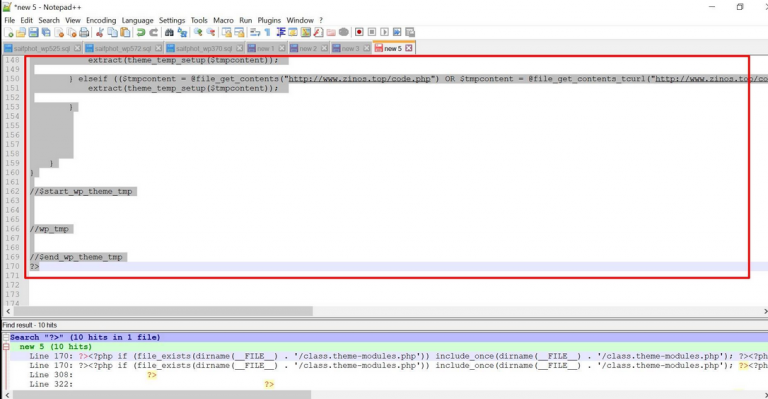
Step::7 Now once you select and delete the first code, the malicious code is now removed successfully. The below part of the code is the real code.
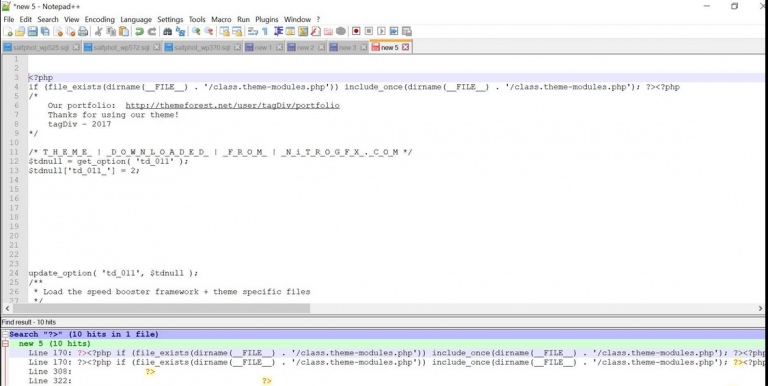
Step::8 Now copy this remaining code and paste it in the original file and then click on Save Changes.
Perform the same procedure for all your other infected files.
Thanks for Reading this article
The End! should you have any inquiries, we encourage you to reach out to the Vercaa Support Center without hesitation.
